SolutionsCompliance
Less to audit. More you can do with regulated data.
Compliance gets harder with every system that holds personal data. Anonomatic keeps PII in one protected place, so audits cover less ground, regulated data stays usable and privacy requests are handled centrally.
-
Shrink your audit scope.
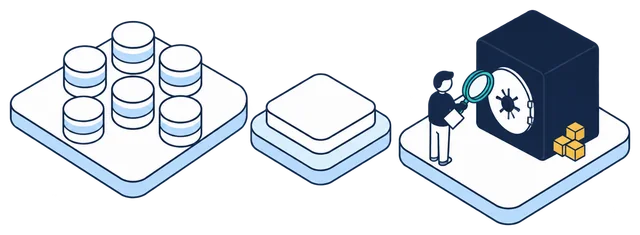
An audit follows the PII. When personal data is spread across every system, every system is in scope.
When PII lives in one protected place instead, SOC 2, FedRAMP and PCI audits have far less ground to cover.
- PII in one protected place
- Far less ground for SOC 2, FedRAMP and PCI audits
PII Vault®
-
Use regulated data without breaking the rules.
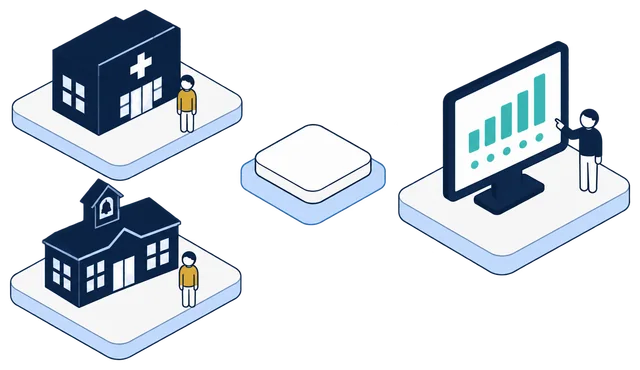
Health records and student records are some of the most useful data an organization holds, and some of the most restricted.
Run full analytics on regulated data, including HIPAA and FERPA data, while it stays fully protected.
- Full analytics
- HIPAA, FERPA and other regulated data
- Fully protected throughout
-
Handle privacy rights requests in one place.
A deletion request is simple to receive and hard to meet when the person’s data sits in system after system.
With Anonomatic, GDPR and CCPA deletion, retention and data-residency obligations are managed centrally instead of system by system.
- Deletion
- Retention
- Data residency
Your data stays in your environment. Anonomatic never receives or sees it.
- Runs in your public cloud, private cloud or on‑premises
- Deploys as a single container
- Fits into your existing systems, no rip‑and‑replace
Use your sensitive data without giving up privacy.
Tell us what you need to do with your data. We’ll show you how Anonomatic can help protect it.